HIPAA and SOC 2 auditors don't check whether you have a policy. They check whether you can produce proof it's being followed: a documented access list with justification, a specific message's handling history, and a retention policy that's actually enforced, not just written down. A shared mailbox that can't produce that evidence isn't compliant just because a policy document says it should be.
Introduction
Compliance and risk officers rarely get surprised by a new regulatory requirement during an audit. What actually catches people off guard is realizing, mid-conversation with an auditor, that a shared mailbox can't answer a question everyone assumed was already covered: who handled this, when did they handle it, and can you show me.
This article isn't a substitute for legal or compliance advice specific to your organization. It's a practical look at what HIPAA and SOC 2 auditors commonly ask for when a shared mailbox is in scope, and what it actually takes to have that answer ready before the question comes up.
What HIPAA auditors typically ask for
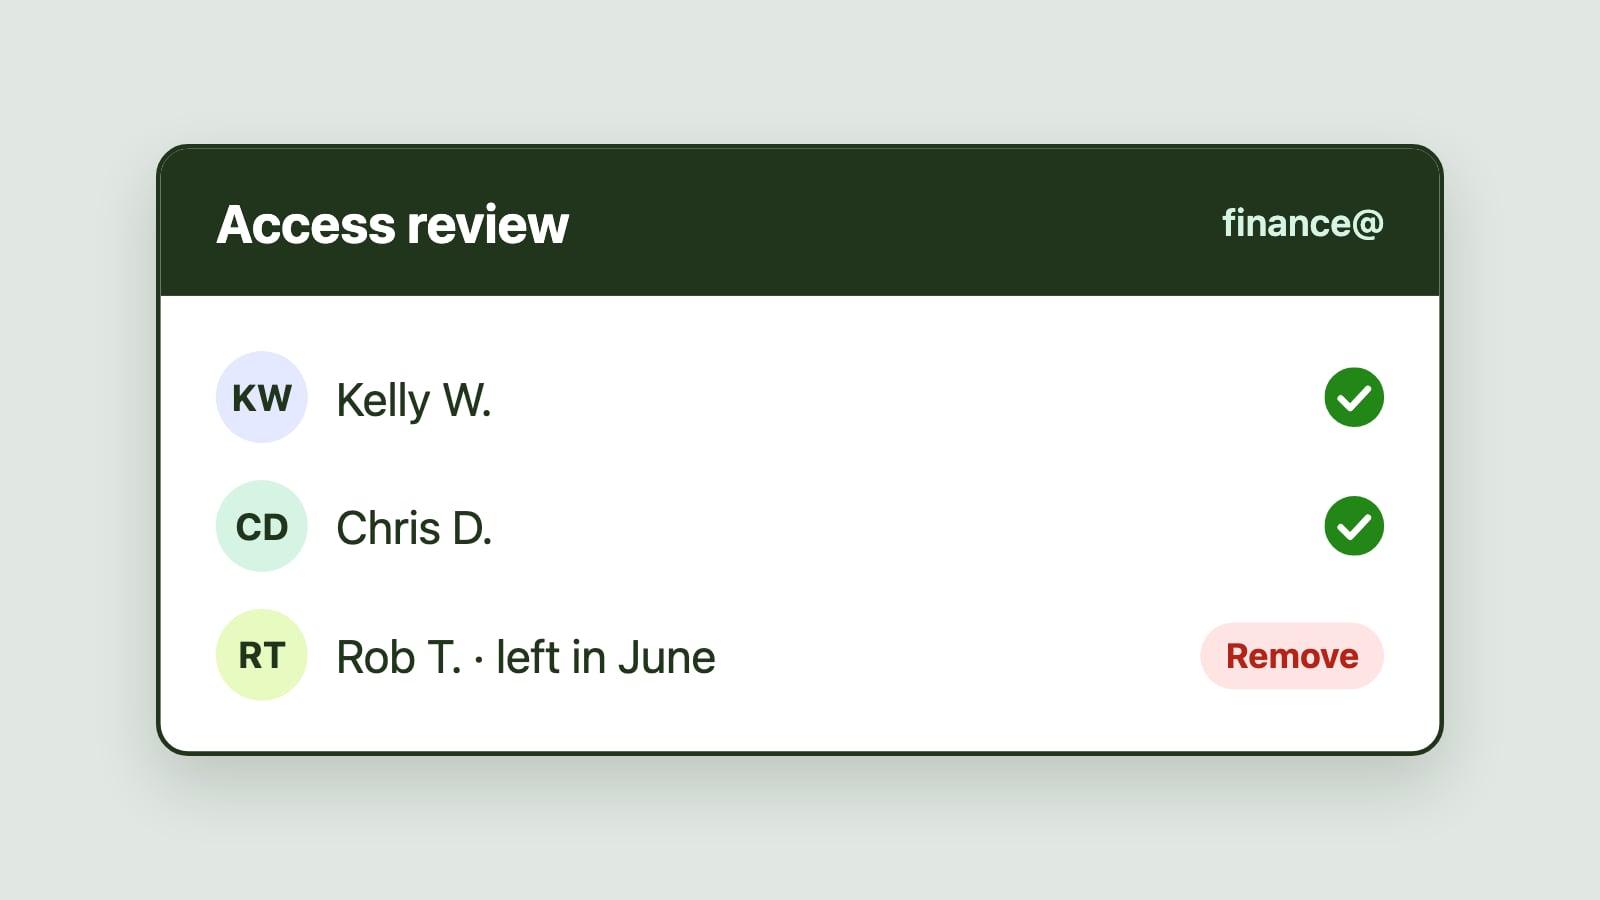
Who has access, and why. Not just a list of names with Full Access or Send As permissions, but a documented justification tied to minimum necessary access. Auditors generally want to see that access reflects an actual business need, reviewed periodically, not a list that's grown by habit.
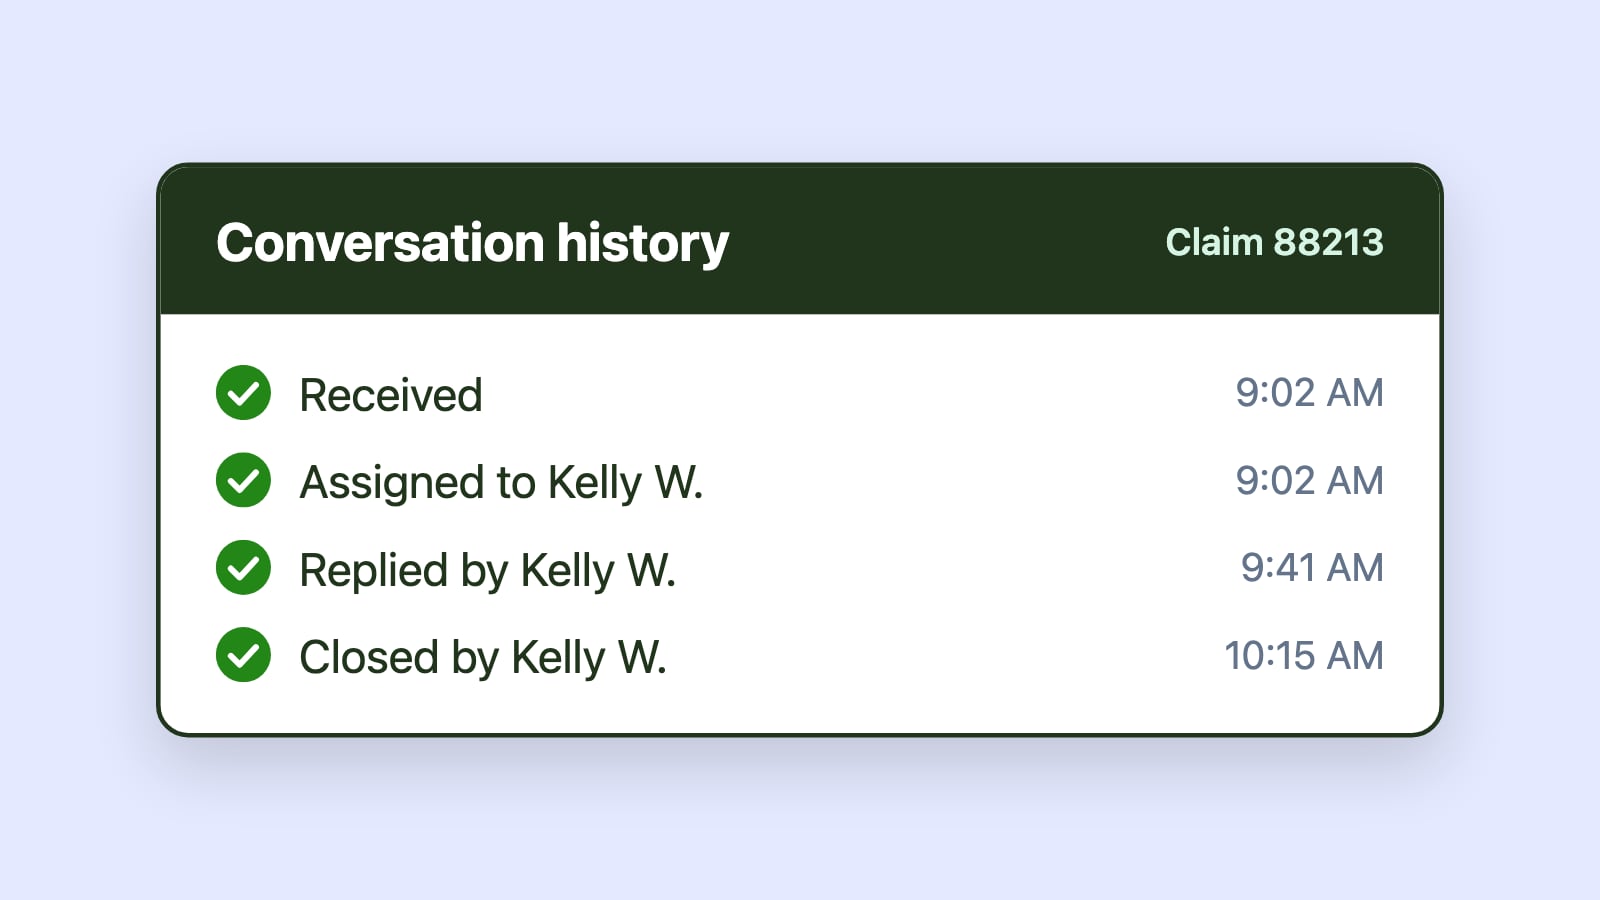
Can you show me who handled this message. For a mailbox that touches protected health information, an auditor may point to a specific message and ask who was responsible for it and when it was addressed. Microsoft's mailbox audit log can show who sent as the mailbox or deleted a message, but a plain shared mailbox has no concept of an owner, so it can't say who was responsible. Anyone with access could have opened, read, or replied to it.
What's your retention and disposal policy. HIPAA compliance generally requires a defined retention period for records containing PHI, along with secure disposal once that period ends. This needs to be documented and demonstrably followed, not just assumed.
Could you reconstruct a disclosure if something went wrong. In the event of a suspected breach, the organization needs to be able to identify what information was involved and who it was disclosed to. Without a clear ownership and activity trail, reconstructing this after the fact becomes a manual, time-consuming exercise, right when speed matters most.
What SOC 2 auditors typically ask for
Evidence of access control, not just an access control policy. SOC 2 audits generally look for documentation showing access reviews actually happen on a regular cadence, not a policy stating that they should.
Logging of user activity. Who did what within the mailbox, and when, maps directly to the monitoring and logging expectations under SOC 2's security criteria. Microsoft 365 mailbox auditing covers part of this, logging actions like sending and deleting that admins can search in Microsoft Purview. What it doesn't show is who owned each message or how assignments changed, so a shared mailbox with no ownership model still leaves gaps here.
Change management records. If permissions changed, when did that happen and who approved it. This is a common gap in mailboxes that have existed for years and accumulated access changes informally.
A demonstrable incident response process. Not just a documented plan, but evidence that the organization could actually execute it, including identifying who was responsible for a given piece of correspondence during the incident window.
The common thread: a record, not a policy
Across both frameworks, the pattern is the same. Auditors are generally satisfied by policies on paper up to a point, but what they're actually testing is whether the organization can produce a record that proves the policy is being followed. Shared mailbox security in regulated industries covers why this distinction matters conceptually; this is what it looks like when someone's actually asking.
A native Microsoft 365 shared mailbox supports access control well and logs actions like sending and deleting, but it has no built-in mechanism for showing who owned a specific message, tracking response times against a regulatory window, or producing a reviewable ownership history. That gap is usually not a sign of poor practices. It's a sign the mailbox was never built to produce this kind of evidence in the first place. Governance structure in Microsoft 365 and how IT teams should structure shared mailboxes both cover the structural side of closing that gap.
What to have ready before an audit
A documented, reviewed access list with justification for each person's access. The ability to pull up a specific message and show who owned it and when it was actioned. A written, enforced retention and disposal policy. And evidence, not just a claim, that response-time commitments tied to regulatory windows are being met.
If you're evaluating a shared mailbox tool partly on its ability to produce this evidence, it's worth knowing that vendor compliance and your own compliance are two different things worth checking separately. Emailgistics holds SOC 2 Type 2 and HIPAA compliance itself, which matters for vendor due diligence, but it's a separate question from whether the tool helps you produce the records your own auditors ask for.
Conclusion
HIPAA and SOC 2 audits rarely ask for anything an organization hasn't already heard of in principle. What they ask for is proof: a specific message's handling history, an access list with justification behind it, a retention policy that's actually enforced. A shared mailbox that was never built to produce that proof isn't a compliance failure by itself, but it does mean the gap is worth closing before an auditor is the one who finds it.